EU AI Act & AI governance platform
Built for developers. Backed by EU AI Act experts.
Ship AI products that pass audit. Automated classification, evidence and monitoring live in your pipeline, and our Berlin team implements ISO 42001, GDPR, ISO 27001, SOC 2 Type II, NIS2 and DORA on the same platform.
Platform + implementation · EU AI Act specialists · Built in Berlin
- CV screening modelRecruiting · ProviderHigh-risk · Annex III
- Credit scoring APILending · DeployerHigh-risk · Annex III
- Support chatbotCustomer service · DeployerLimited · Art. 50
- Code assistantEngineering · DeployerMinimal risk
EU AI Act Timeline: GPAI obligations active from Aug 2025 · High-risk obligations from 2 Dec 2027 (Annex III) and 2 Aug 2028 (Annex I products) · Penalties up to €35M or 7% global turnover.
Seven regulations. Seven spreadsheets. One overloaded team.
Your AI Act assessment lives in one file, your GDPR register in another, your ISO 27001 controls in a third. Your biggest customer just sent a SOC 2 questionnaire. Most of it is the same work: access control, logging, risk assessment, supplier checks. You are doing it over and over.
Two ways to work with us
A platform your engineers adopt. Experts your auditors trust.
Use the platform on its own, bring in our team, or both. Either way, it is one inventory, one evidence base and one set of controls.
The platform
Built for developers
Integrate once and run forever: classification via API, evidence via vault, documentation via generator.
The experts
Came for the AI Act? We handle the rest.
Most clients start with AI governance. Soon a customer asks for ISO 27001, a US deal needs SOC 2, or a regulator asks about NIS2 or DORA. Our team extends what you already have.
Why AnnexOps
Built for AI businesses. Backed by AI governance experts.
How it works
From zero to audit-ready in 5 steps
The guided compliance journey takes you from your first AI system to your first health score, and our experts are there whenever you want a hand.
-
Discover your AI
Connect your cloud, code and apps, or import from GitHub, SageMaker or HuggingFace via SDK. AnnexOps builds a live inventory of every AI system, model and AI vendor.
-
Classify
Each system gets an EU AI Act risk class and provider or deployer role, with documented reasoning against all 8 Annex III categories.
-
Map obligations
Obligations come with article references and owners, and every control is mapped across every framework you need at once.
-
Document and prove
Generate Annex IV, QMS and DPIA documents, your ISO Statement of Applicability and SOC 2 packages. Collect evidence once in the tamper-evident vault.
-
Stay compliant
Share your Compliance Health Score, export audit packages for auditors and regulators, and embed your Compliance Badge.
Product Features
Everything You Need to Prove Compliance
From risk classification to a tamper-evident evidence vault, AnnexOps gives AI teams the full toolchain to meet the EU AI Act and GDPR — automated, auditable, and built into your pipeline.
Annex III · All 8 Categories
We classify every risk level the EU AI Act defines
Prohibited · Art. 5
Unacceptable Risk
AI systems banned outright. In force since February 2, 2025.
High risk · Annex III
Full Obligations Apply
Extensive requirements including technical docs, conformity assessment, and EU registration.
Limited risk · Art. 50
Transparency Obligations
Disclosure requirements when interacting with AI or generating synthetic content.
Minimal / GPAI
Low Obligations
General purpose AI with systemic risk obligations active from August 2025.
Stricter tiers at the top. AnnexOps classifies each AI system against all 8 Annex III use-case categories to find its tier.
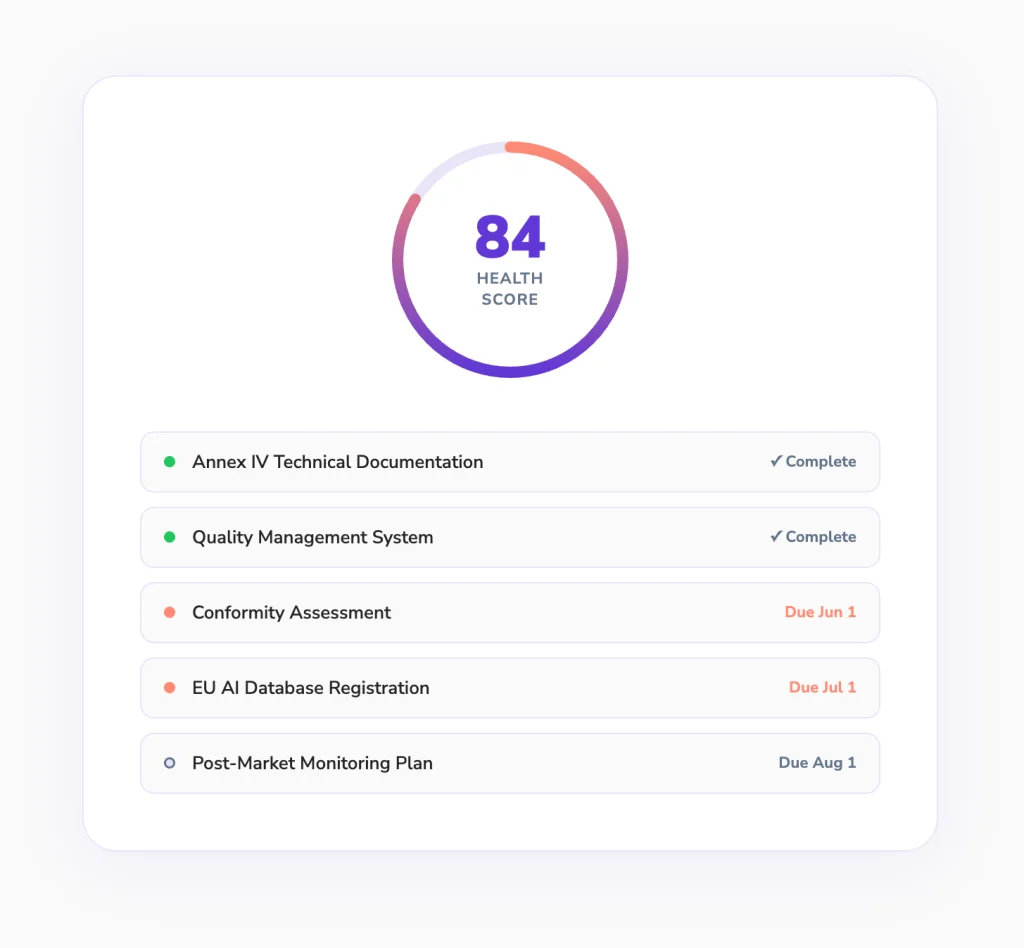
Compliance Health Score
A single number your board will understand
Real-time 0–100 score computed from obligation completion, monitoring events, and evidence status. Updated continuously. Shareable with investors, clients, and regulators.
Developer SDK
Compliance that lives in your pipeline
The AnnexOps SDK installs in 2 minutes. It auto-registers AI systems, runs continuous compliance checks, and streams telemetry to your dashboard. Free forever for open source.
Evidence Vault
The Audit Chain EU Regulators Demand
Who it is for
Know your real deadlines
The AI Act is already in force. Is your AI inventory ready?
Prohibited AI practices and AI literacy duties apply since February 2025. Transparency rules for chatbots and AI-generated content apply now. High-risk obligations apply from 2 December 2027. Building an audit-ready AI programme takes months, so start now.
On track · 2026
2 Aug 2026
Transparency rules take effect, and every member state must have a regulatory sandbox up and running.
In effect now
Pushed back · New date
2 Dec 2027
The major high-risk AI obligations everyone was bracing for now land here.
In effect now
Pushed back · New date
2 Aug 2028
High-risk rules for AI embedded in other regulated products — like medical devices.
In effect now
All deadlines 23:59 CET (UTC+1). Source: EU AI Act, Digital Omnibus revisions.
Integrations
Works With Your Existing Stack
- GitHub Actions
- GitLab CI
- HuggingFace
- Anthropic Claude
- Mistral AI
- AWS SageMaker
- Grafana
- Jira
- Linear
- Slack
- Google Vertex AI
- OpenAI API
FAQs
Some Frequently Asked Questions and Their Answers
What makes AnnexOps different from traditional AI compliance tools?
Most AI compliance tools focus on documentation and periodic audits. AnnexOps is designed as a full AI governance platform for EU AI Act compliance, enabling organizations to continuously discover AI systems, classify risk, and monitor behavior across their infrastructure. This makes it more suitable for enterprises managing multiple AI systems at scale.
How does AnnexOps help with EU AI Act compliance for enterprises operating in Europe?
AnnexOps helps organizations meet EU AI regulation compliance requirements by providing a centralized system to track AI usage, classify systems under risk categories, and maintain audit-ready documentation. It supports both AI providers and deployers, ensuring alignment with EU regulatory expectations.
How does AnnexOps perform AI risk classification under the EU AI Act?
AnnexOps uses a structured AI risk classification tool aligned with EU AI Act guidelines, evaluating systems based on use case, impact, and deployment context. This ensures accurate classification across minimal, limited, and high-risk categories.
Can AnnexOps automate AI compliance processes across multiple systems?
Yes. AnnexOps acts as an AI compliance automation platform, enabling organizations to automate system discovery, risk classification, monitoring, and documentation generation. This reduces manual effort and ensures consistent compliance across all AI systems.
What type of organizations should use AnnexOps AI governance platform?
AnnexOps is designed for enterprises deploying AI systems, SaaS companies offering AI features, organizations operating in Europe, and companies preparing for EU AI Act compliance. It is particularly useful for organizations managing multiple AI systems across teams.
Read Our Blog